


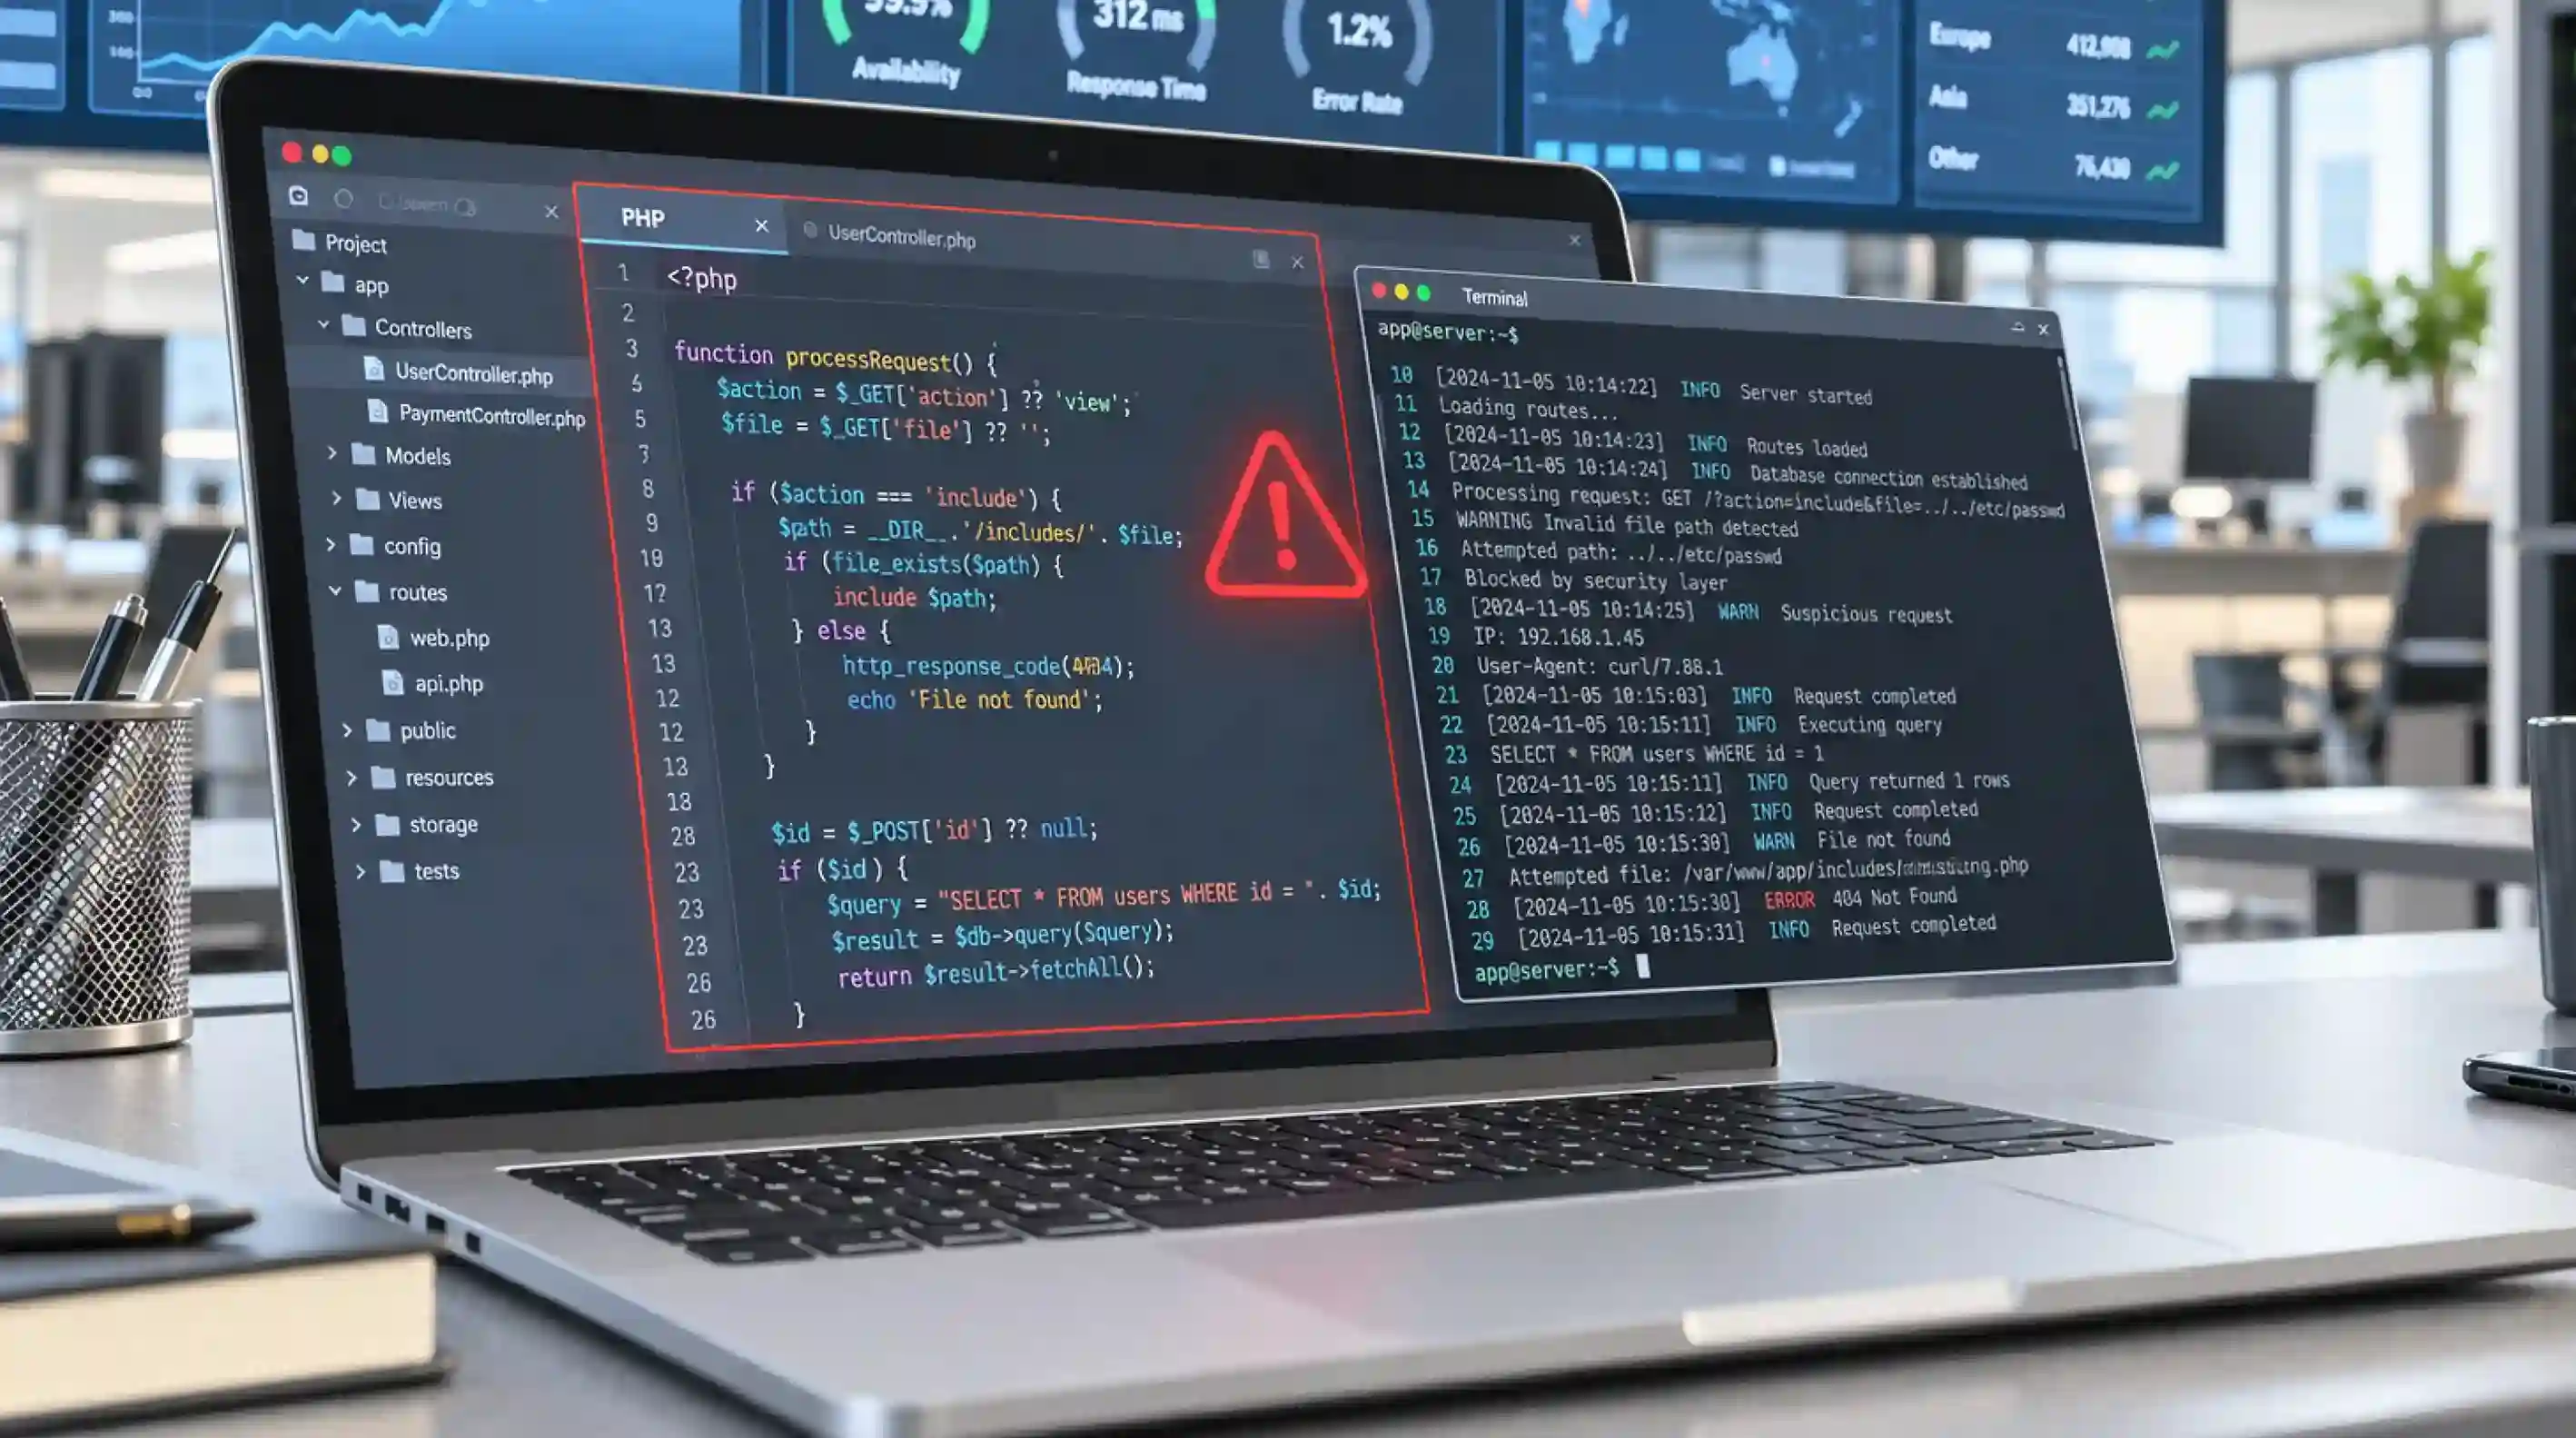

PHP2Shell Exposure Alert: NeoSOFT Steps In to Lock Down Vulnerable Enterprise Applications
Mumbai, India, 27 October 2026: Digital engineering firm NeoSOFT is actively working alongside enterprise clients to evaluate and fix security risks tied to the recent PHP2Shell vulnerability. Delivered through its specialized Cybersecurity Centre of Excellence (CoE), the program gives companies a practical way to audit application stacks, measure real exposure, and roll out effective technical solutions.
For banks, financial services, NBFCs, and large commercial operations, a software vulnerability is rarely just a technical concern. A single security gap can freeze core operations, leak protected client records, and damage institutional reputation overnight. The real challenge hits the moment a critical bug is made public. Internal IT teams must quickly figure out whether their application stack is exposed, how deep the vulnerability goes, and what steps to take first.
Addressing the issue, Nishant Rathi, Founder & Director at NeoSOFT, said:
“When a new vulnerability hits the news, companies first need to figure out if it actually affects them. You cannot make smart decisions or gauge urgency until you know your real exposure. We step in to help teams map out their exact risks and prioritize their next moves, whether that means spotting an exposed app right away or fixing high-priority flaws without breaking daily operations. Every setup is different, so we focus on practical steps that protect the business without slowing it down.”
Core Areas of Technical Support
NeoSOFT’s security practice works directly with enterprise teams through four main focus areas:
- Exposure Scans – Locating exposed code paths, open endpoints, and vulnerable application libraries fast.
- Impact Rating – Assessing actual severity based on core business risks rather than generic threat scores.
- Patch Management – Designing and applying stable security updates built to fit complex existing software environments.
- Validation Checks – Conducting thorough post-remediation testing to ensure security gaps are fully closed without breaking existing functionality.
CMMI Level 5 Engineering Rigor Applied to System Defense
Building on over 25 years of enterprise software engineering, NeoSOFT brings high-maturity operational context to vulnerability management. Appraised consecutively three times at CMMI Level 5 for software development, the firm follows strict process benchmarks across application design, deployment, and security hardening. Because NeoSOFT engineers, builds, and maintains large-scale digital platforms, its technical teams understand how backend runtimes interact with underlying infrastructure. This hands-on engineering background allows NeoSOFT to implement security updates that protect critical systems while maintaining continuous uptime.
Organizations seeking to evaluate their infrastructure for PHP2Shell vulnerability exposure can reach out directly to NeoSOFT’s Cybersecurity CoE for an initial technical assessment.